Thousands of Android Phones Ship With Hidden Malware That Disables Google Play Protections
 This story is only covered by news sources that have yet to be evaluated by the independent media monitoring agencies we use to assess the quality and reliability of news outlets on our platform. Learn more here.
4 Articles
4 Articles

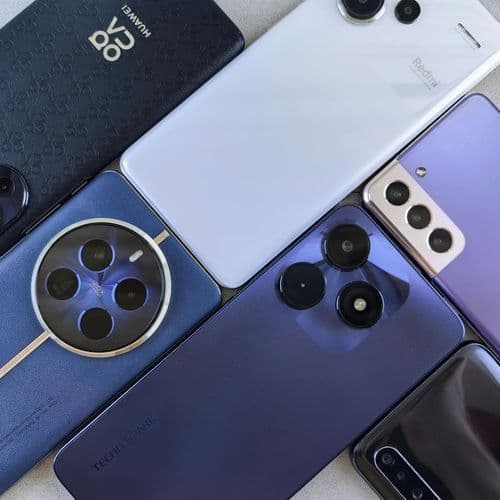
Bitdefender's security experts have discovered some inexpensive Android smartphone models that are shipped with malware. The malware is embedded in the cell phone firmware, so buyers of such phones receive a brand-new device on which the malware is already installed. The experts call this attack wave Midnight Mimosa. Using the pre-installed malware that has system-level rights, attackers can unnoticedly install apps, commit ad fraud, and turn de…

Thousands of Android Phones Ship With Hidden Malware That Disables Google Play Protections
Thousands of Android phones across more than 150 countries have been found running malware planted in their firmware before purchase. The campaign, called Midnight Mimosa, targets low-cost devices and gives attackers system access without requiring owners to download a harmful app or click a suspicious link. The malware can secretly install and remove apps, load […]
 cybernoz.com
 IT Security News - cybersecurity, infosecurity news
Hackers Turn Low-Cost Android Phones Into Hidden Proxy Botnets Through Preinstalled Malware
Midnight Mimosa, a widespread Android malware campaign, is turning inexpensive smartphones into advertising fraud engines and potential residential proxy nodes by embedding malicious apps in device firmware before purchase. Bitdefender observed thousands of infected devices across more than 150 countries over approximately two years, exposing a persistent compromise that ordinary application removal cannot resolve. The
Coverage Details
Bias Distribution
- There is no tracked Bias information for the sources covering this story.


Factuality
To view factuality data please Upgrade to Premium