Pentagon HR Breach Exposes Unencrypted Military Data; Scope Unclear
United States
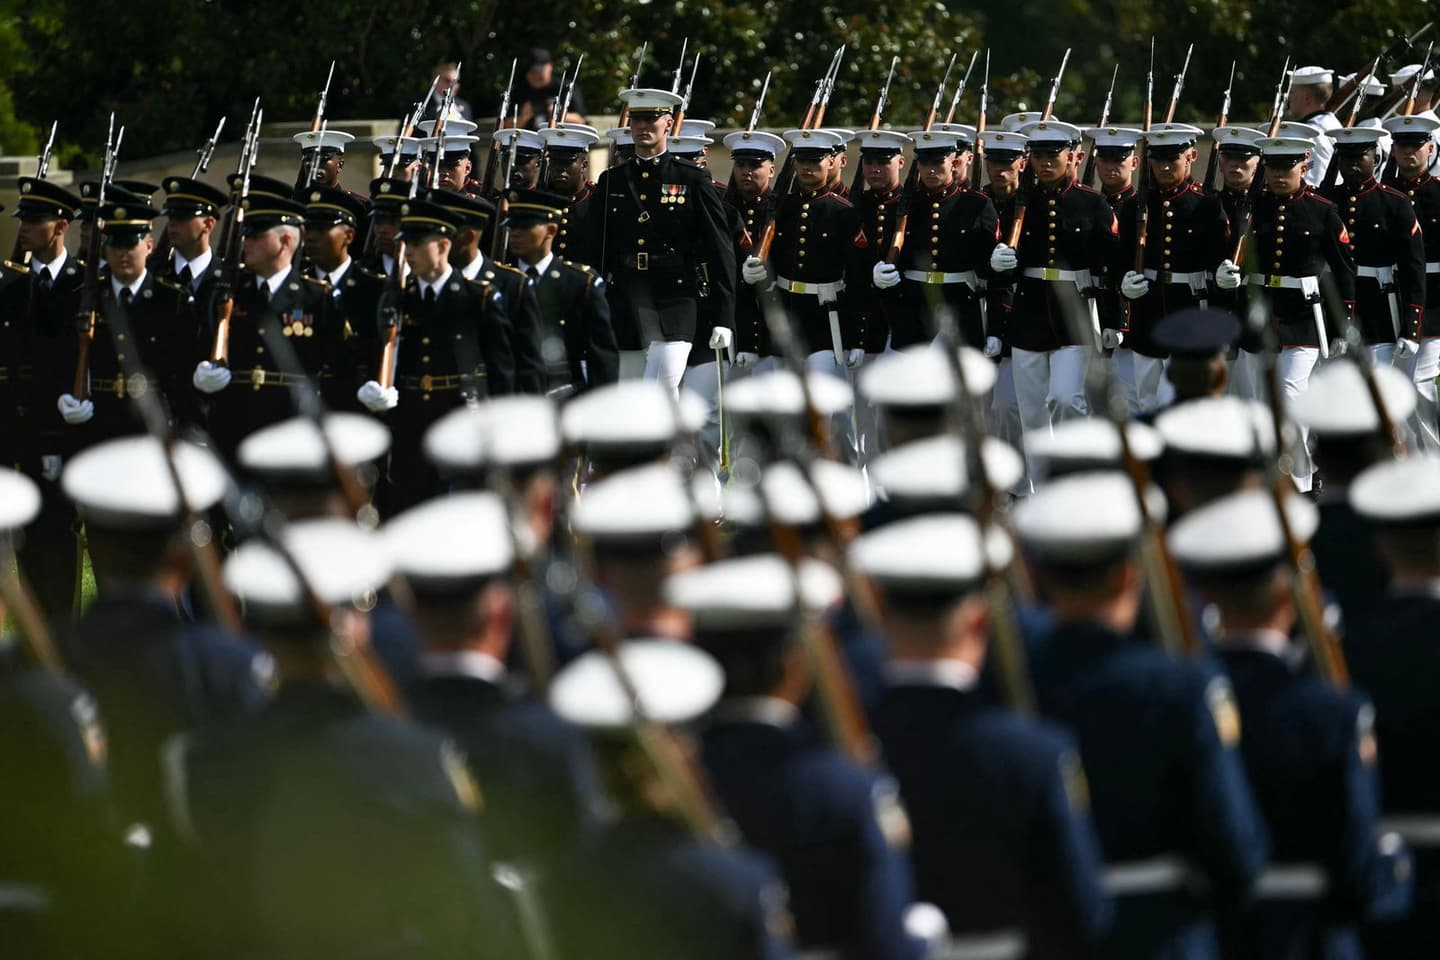
Kent NISHIMURA / AFP via Getty Images/Getty
Source Analysis
What Happened
What Happened
Where Sources Agree
- arrows_inputBreach Timeline and Nature: Sources across outlets confirm unauthorized users accessed unencrypted personal data through a file-sharing system vulnerability between October 2025 and July 2026, a breach that went undetected for nine months, according to a notification letter.
- arrows_inputScale of Data Breach: Reports consistently note that approximately four million Defense Department personnel may be affected by the recent data breach, with exposed files containing Social Security numbers and occupational specialties, according to breach notification letters and media reports.
- arrows_inputPentagon Response and Mitigation: Sources align on the Pentagon’s mitigation measures following the DMDC data breach, noting the agency has patched the file-sharing system and is offering one year of credit monitoring, while currently seeing no indications of misuse, according to the DMDC notification letter.
Where Sources Disagree
- arrows_outputBreach Risk Framing: While some reports emphasize the national security implications of the breach given the ongoing war with Iran, others focus on the immediate technical risks of identity theft and the scope of exposed personnel records.
- arrows_outputPersonnel Breach Scope: Military Times sources report that approximately four million Defense Department personnel may be affected by the breach. However, other outlets and official assessments indicate that the total scope of affected individuals remains unclear.
Timeline
September 18, 2026
Notifications, Response, Concerns: DMDC sent notifications (notably a Sept. 18 letter to at least one victim), is offering one year of credit monitoring and identity‑restoration services through IDX, and says a broader "cyber hunt" led by Defense Information Systems Agency director Gen. Paul Stanton is underway; the Pentagon currently reports no indications of misuse. Experts warn the exposed trove raises counterintelligence risks and uncertainty persists about the culprit and full scope.
July 16, 2026
Unencrypted PII Exposed: The breach exposed unencrypted data including Social Security numbers, at least one other identifier (name, DOB, contact info, sex, race or military occupational specialty), and in some reports could affect up to four million DoD personnel. Reporting notes the records were not encrypted and the exact number impacted remains unclear.
July 16, 2026
Vulnerability Discovered and Patched: DMDC discovered the file‑sharing vulnerability on July 16, 2026, updated the system to patch the flaw and restored the service, according to a notification sent to affected individuals. The remediation followed an internal analysis of the exposed server.
Summary by Ground AI
Sources
See All 21A varied selection of sources chosen by Ground to reflect the diversity of this story’s coverage.
Most Written About
The stories getting the most coverage from the last 24 hours


Source Analysis
Timeline
September 18, 2026
Notifications, Response, Concerns: DMDC sent notifications (notably a Sept. 18 letter to at least one victim), is offering one year of credit monitoring and identity‑restoration services through IDX, and says a broader "cyber hunt" led by Defense Information Systems Agency director Gen. Paul Stanton is underway; the Pentagon currently reports no indications of misuse. Experts warn the exposed trove raises counterintelligence risks and uncertainty persists about the culprit and full scope.
July 16, 2026
Unencrypted PII Exposed: The breach exposed unencrypted data including Social Security numbers, at least one other identifier (name, DOB, contact info, sex, race or military occupational specialty), and in some reports could affect up to four million DoD personnel. Reporting notes the records were not encrypted and the exact number impacted remains unclear.
July 16, 2026
Vulnerability Discovered and Patched: DMDC discovered the file‑sharing vulnerability on July 16, 2026, updated the system to patch the flaw and restored the service, according to a notification sent to affected individuals. The remediation followed an internal analysis of the exposed server.


